Alerts without clear priorities
Vulnerability alerts are piling up, but it is unclear which fixes cannot wait.

The review covers the agreed parts of the application and development process. For web applications, we use the relevant OWASP ASVS requirements. The findings specify what to fix and why some issues take priority.
Documented findings and remediation proposals can also support meeting the relevant technical requirements of the Cyber Resilience Act (CRA) and NIS2.
Vulnerability alerts are piling up, but it is unclear which fixes cannot wait.
It is difficult to establish who can access data and how access keys are managed.
Security gaps only surface before release, when fixing them can delay deployment.
The report lists the areas reviewed and gives the evidence behind each finding.
Priorities reflect both technical risk and business consequences, so it is clear which fixes are urgent.
Developers and operations staff receive specific tasks and the checks needed to verify each fix.
Can users access only the data they need for their tasks?
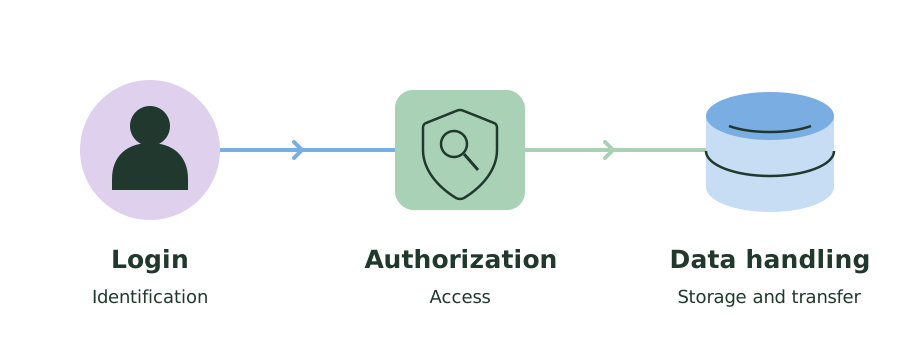
Each step has different potential errors and consequences.
Application, access, authorized methods
Dependencies, permissions, release process
Priorities, owners, verification
This service is a technical review. Penetration testing requires a separate agreement and a specialist partner.
Unsure about permissions, data handling or system dependencies? Let's discuss which areas would benefit most from a review now.
The first 30-minute conversation is without obligation. We arrange a time by email.
Let's talkcontact@core-systems.hu